

The SMS OTP signature is based on a one-time-password code, generated from the hash of the document to be signed, and sent to the signer’s cell phone via SMS. The verification code generated by Viafirma corresponds to a random algorithm for which the content of the document to be signed (hash) is used, being able to prove that this OTP code corresponds to a specific document and not to another one.
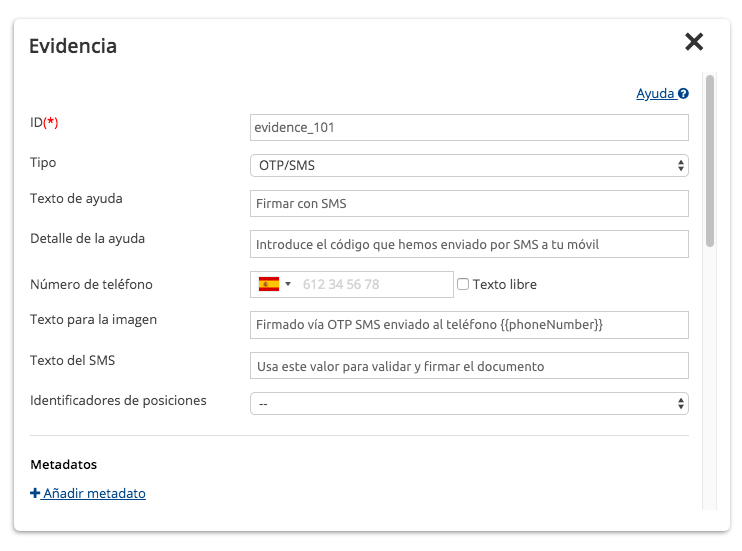
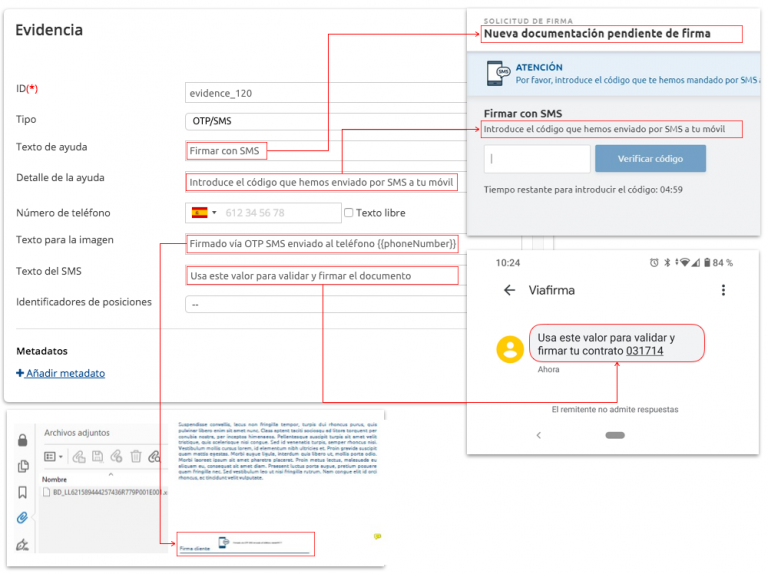
An example configuration for this type of evidence could be:
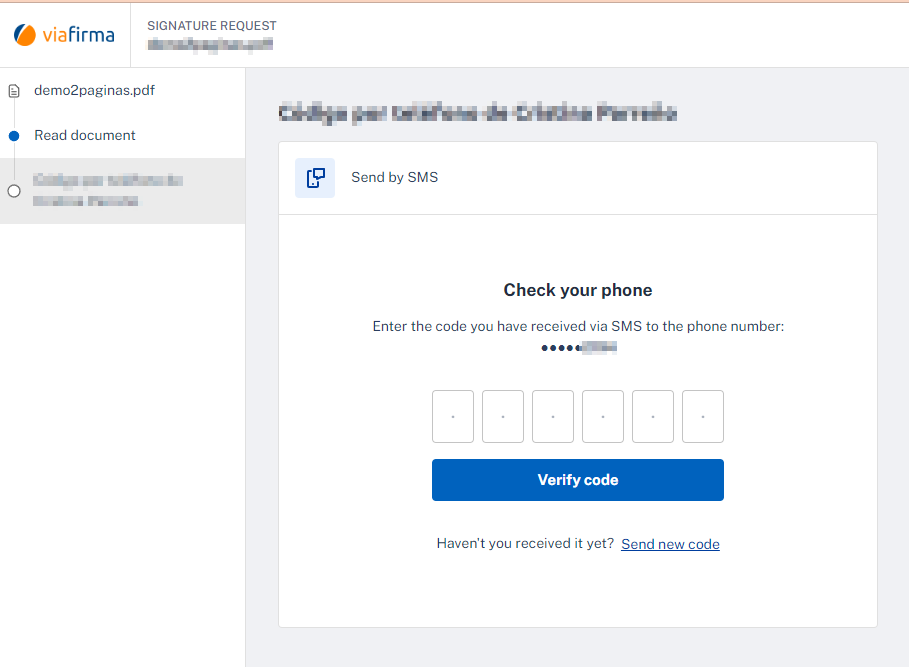
During the signing process, the signer will be shown as follows:
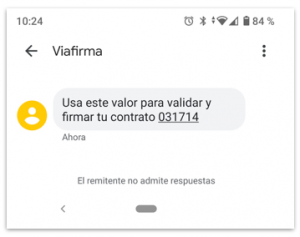
This is the SMS you will receive to tell you the code to enter:
Once the signature has been made, the result will be as follows.
Document where the evidence is shown:
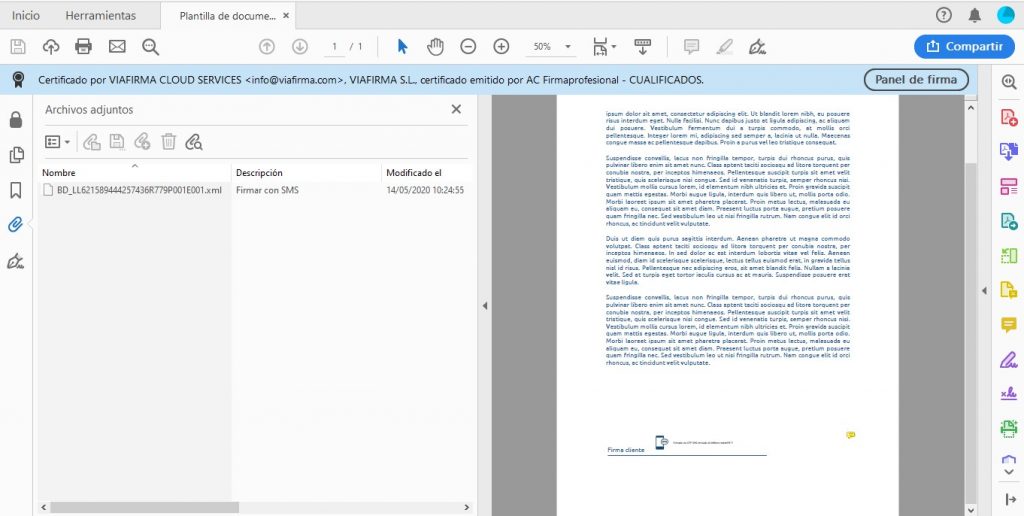
Data collected during the signature and that can be seen from the document itself if in the evidence we activate the option “Add public link on the evidence”:
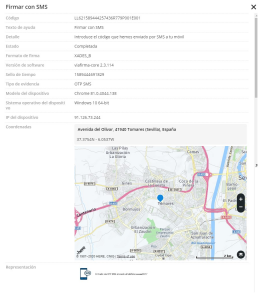
This information will be available at all times from the platform.
As a summary and to see how the configuration would affect the signature process, let’s see the following image:
LINK OF INTEREST:
If you have any questions about the use of this information please contact us directly.